28
SPF Record Explained: What Is SPF and How Does Email Authentication Work
Learn what an SPF record is, how SPF works with DNS TXT records, what common SPF mechanisms mean, and how to avoid errors in your domain's email authentication setup.
When you send an email from your domain, how does the receiving mail server know whether the sending server is allowed to send it? One important part of the answer is SPF.
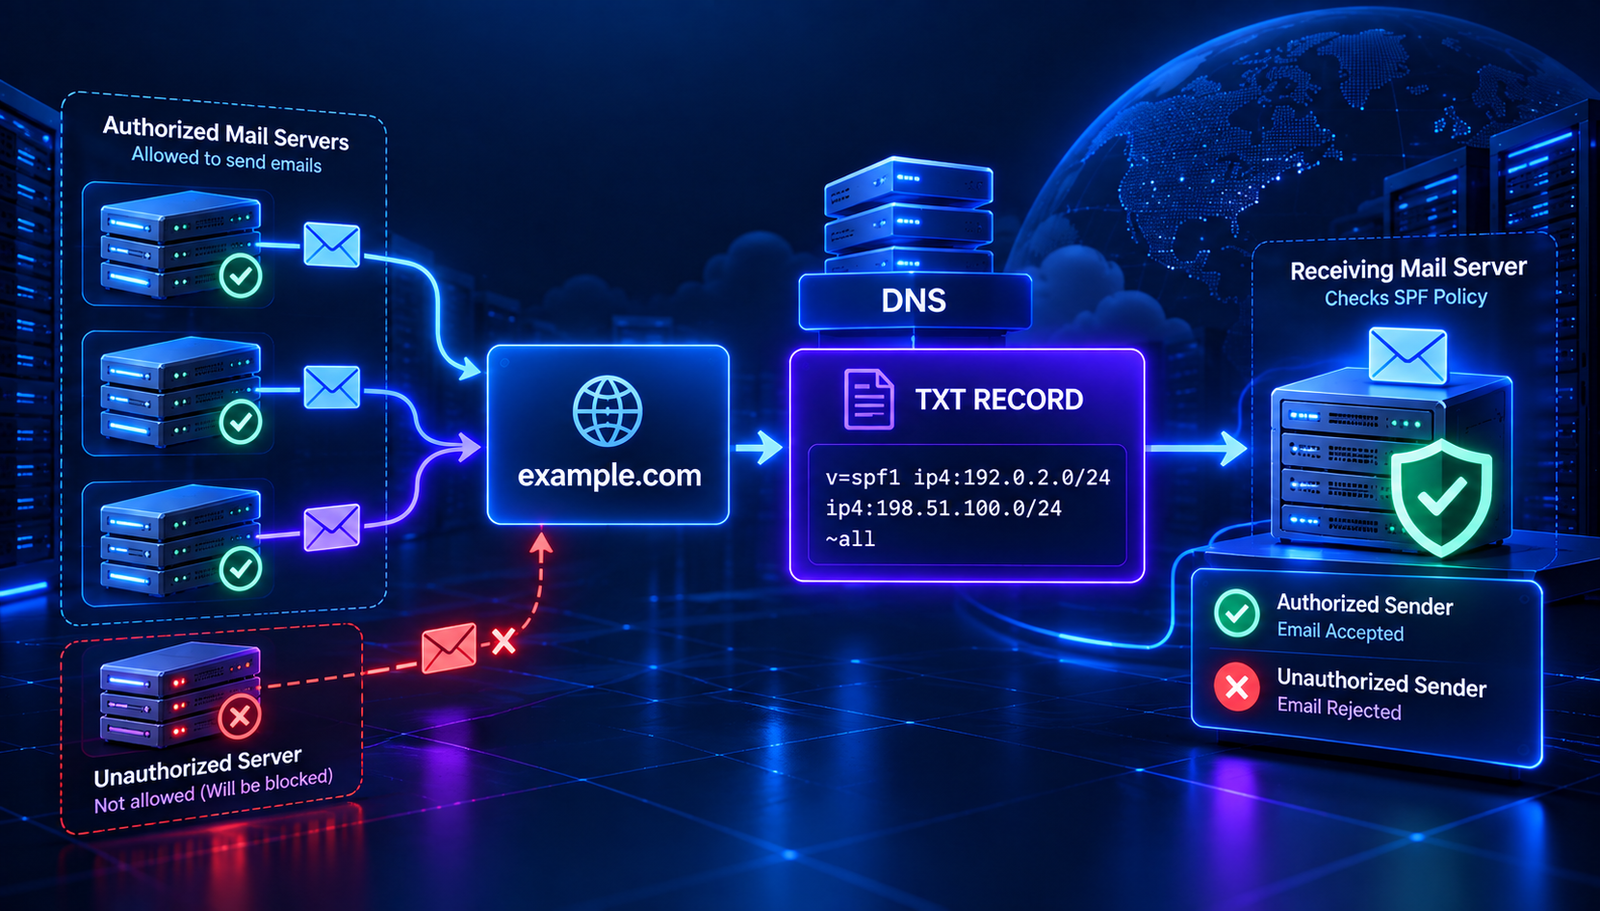
SPF stands for Sender Policy Framework. It is an email authentication method that lets a domain publish a list of authorized sending sources in DNS. Receiving mail servers can check this policy when evaluating incoming messages.
In this guide, you will learn what an SPF record is, how it works, what its common mechanisms mean, and how to avoid mistakes when setting it up.
What Is an SPF Record?
An SPF record is a DNS TXT record that describes which mail servers and sending services are permitted to send email using a domain's sending identity.
For example, if you use a business email provider and a separate newsletter platform, your SPF policy may need to account for both services. The receiving server can check the published policy to see whether the sending source is authorized.
SPF does not use a separate DNS record type in normal modern configurations. Instead, the policy is published as text in a TXT record.
How Does SPF Work?
SPF is checked during the email delivery process. The receiving mail server evaluates the sending server's IP address against the SPF policy for the relevant domain identity, commonly the domain used in the SMTP MAIL FROM command.
- You send an email through a mail server or email service.
- The receiving server gets the message and identifies the relevant sending domain.
- It looks up that domain's SPF policy in DNS.
- It evaluates the sending IP address against the policy's mechanisms.
- The check produces a result such as pass, fail, softfail, neutral, or none.
The receiving server decides how to handle the result. SPF passing does not guarantee that a message reaches the inbox. Other checks and the receiver's own policies also matter.
What Does an SPF Record Look Like?
A simple SPF record may look like this:
v=spf1 ip4:192.0.2.10 -all
This example says that the listed IPv4 address is authorized and that other sources should receive a fail result under the policy.
This is an illustrative example using a documentation-only IP address. Do not copy it into your domain unless it matches your actual mail setup.
Common SPF Mechanisms and Terms
An SPF policy is made up of mechanisms and qualifiers. Each part helps define which sources match the policy.
1. v=spf1
This identifies the record as an SPF version 1 policy. It should appear at the beginning of the SPF record.
2. ip4
The ip4 mechanism authorizes a specific IPv4 address or range.
v=spf1 ip4:192.0.2.10 -all
3. ip6
The ip6 mechanism authorizes a specific IPv6 address or range.
v=spf1 ip6:2001:db8::10 -all
4. a
The a mechanism checks the address records for a domain. If the connecting IP matches an address returned by the relevant lookup, it matches this mechanism.
v=spf1 a -all
5. mx
The mx mechanism checks the IP addresses associated with the domain's mail exchanger hosts.
v=spf1 mx -all
Using mx does not automatically authorize every service you use to send email. It only checks the hosts associated with the domain's MX records.
6. include
The include mechanism lets your policy incorporate another domain's SPF policy. It is commonly used when an external email service sends messages on your behalf.
v=spf1 include:example-provider.com -all
Use the exact include value supplied by your email provider. Adding an incorrect domain or unnecessary include can cause authentication problems.
7. all
The all mechanism matches any source that has not matched an earlier mechanism. It is often placed at the end of the policy.
The character before all determines the result:
- -all means fail.
- ~all means softfail.
- ?all means neutral.
- +all means pass for all sources and is generally not suitable as a restrictive SPF policy.
Read More: Related DNS Guides
- MX Record Explained: How Email DNS Works — understand how domains direct incoming email to mail servers.
- TXT Record Explained: DNS Verification — learn how TXT records store domain-related text information.
- DNS Lookup: How to Check DNS Records — learn how to inspect DNS records for a domain.
SPF Qualifiers Explained
A qualifier tells the SPF evaluator what result to return when a mechanism matches.
- + Pass: the source is authorized by this mechanism. This is the default when no qualifier is written.
- - Fail: the source is not authorized under this mechanism.
- ~ Softfail: the source is not authorized, but the policy signals a less definitive failure.
- ? Neutral: the policy makes no assertion about the source.
For example, ~all and -all are not interchangeable. The result is part of the policy you publish, and receiving systems may handle those results according to their own rules.
How to Add an SPF Record to Your Domain
The exact steps depend on where your DNS is hosted. You may manage DNS through your domain registrar, hosting provider, or a separate DNS service.
- Identify every service that sends email for your domain. Include your mailbox provider, website application, CRM, and marketing platform if they send mail using your domain.
- Collect each provider's SPF instructions. Use the exact mechanisms or include domains they specify.
- Review your existing TXT records. Check whether an SPF policy already exists for the hostname you are configuring.
- Create or update the SPF TXT record. The host/name is often the root domain, represented by @ in many DNS dashboards, but follow your provider's instructions.
- Save the record and allow DNS time to update. The time required depends on DNS caching and the record's TTL.
- Check the published record and test your email. Confirm that the policy is visible and that legitimate sending services are accounted for.
Important SPF Rule: Avoid Multiple SPF Records
A hostname should not publish multiple separate SPF policies. If you have several services sending email, their authorized sources generally need to be combined into one SPF record for that hostname.
For example, publishing two TXT records that each begin with v=spf1 can cause SPF evaluation to return a permanent error. Do not simply add a second SPF record when a new provider asks you to configure one. Review the existing policy and merge the required mechanisms carefully.
Understand the SPF DNS Lookup Limit
SPF has a limit of 10 DNS-query-causing terms during a single evaluation. Mechanisms and modifiers such as include, a, mx, exists, and redirect can contribute to this limit.
If a policy exceeds the limit, SPF evaluation can return a permerror. This is one reason to avoid unnecessary includes and complicated chains of third-party policies.
Do not assume that counting the visible words in a record is enough to validate the lookup limit. Nested policies can add further DNS lookups during evaluation.
SPF vs. DKIM vs. DMARC
SPF is one part of email authentication. DKIM and DMARC address related but different aspects.
- SPF: checks whether the sending source is authorized by the domain's SPF policy for the evaluated SMTP identity.
- DKIM: uses a cryptographic signature to help verify that a message was signed by a domain and that signed parts have not been altered.
- DMARC: tells receiving systems how to handle messages that fail DMARC evaluation and provides reporting options. It also checks alignment between authenticated domains and the visible From domain.
These methods work together, but none should be treated as a guarantee that a message is safe or will be delivered to the inbox.
Common SPF Errors and How to Fix Them
1. Publishing two SPF records
Problem: More than one TXT record starts with v=spf1 for the same hostname.
Fix: Combine the authorized sending sources into one policy. Remove obsolete or duplicate SPF records after checking which services still send email.
2. Forgetting a sending service
Problem: Your mailbox provider is included, but your website or newsletter service is not.
Fix: Make a complete list of services that send using your domain and follow each provider's current DNS instructions.
3. Exceeding the DNS lookup limit
Problem: Too many DNS-query-causing terms are evaluated, sometimes because of nested includes.
Fix: Review the SPF policy and its included policies. Remove unnecessary sources and simplify the configuration where possible.
4. Using the wrong include domain
Problem: An include value is mistyped or belongs to a different service.
Fix: Copy the exact value from the provider's official setup instructions and verify that the provider still recommends it.
5. Editing the wrong hostname
Problem: The SPF record is published for a subdomain while the email service uses the root domain, or the reverse.
Fix: Confirm which domain appears in the SMTP sending identity and follow the provider's hostname instructions.
How to Check an SPF Record
You can inspect the TXT records published for your domain using a DNS lookup tool. Search for the TXT record that begins with v=spf1 and review its contents.
For a command-line check, you can use:
dig example.com TXT
Or:
nslookup -type=TXT example.com
Replace example.com with your own domain. If your DNS provider supports it, you can also inspect the record in its DNS management dashboard.
Use the AuraTools DNS Lookup to inspect DNS information for a domain. Check that the TXT result contains the SPF policy you expect. A DNS lookup confirms what is published; it does not by itself prove that every sending service is configured correctly.
SPF Best Practices
- Publish one SPF policy per hostname.
- Authorize only services that actually send email using that domain.
- Use the exact configuration values provided by your email services.
- Keep the policy within SPF's DNS lookup limit.
- Remove obsolete sending sources after confirming they are no longer needed.
- Review SPF whenever you add or replace an email provider.
- Use DKIM and DMARC as complementary email authentication methods.
- Test real messages and review authentication results from receiving systems.
Frequently Asked Questions
Is SPF a TXT record or a separate DNS record type?
SPF policies are normally published in DNS TXT records. The policy begins with v=spf1.
Can I have two SPF records for one domain?
You should publish one SPF policy for a given hostname. If multiple services send email, combine their authorized sources into that single policy rather than creating multiple SPF records.
Does SPF stop email spoofing?
SPF can help receiving servers identify whether a sending source is authorized for the evaluated domain identity. It does not independently prevent every form of spoofing, and it does not directly authenticate the visible From address in every case. DMARC adds alignment checks involving the visible From domain.
Does SPF improve email deliverability?
Correct SPF configuration can help receiving systems authenticate legitimate email. Deliverability also depends on factors such as domain reputation, message content, recipient engagement, sending practices, and other authentication checks.
What does SPF softfail mean?
Softfail, commonly written as ~all, indicates that a source did not match an authorized mechanism, but the policy is expressing a less definitive failure than -all. Receiving systems decide how to handle the result.
How long does an SPF record take to update?
There is no single fixed time. DNS caching and TTL settings affect when changes become visible to different resolvers. Check the published record after making changes and allow time for cached results to expire.
Conclusion
An SPF record helps your domain publish which sources are allowed to send email using its sending identity. A correct policy can support email authentication, but it needs to reflect your real sending setup and stay within SPF's technical limits.
Start by listing every service that sends email for your domain. Check whether an SPF record already exists, combine the required sources into one policy, and verify the published TXT record. For broader email protection, configure DKIM and DMARC as well.
Contact
Missing something?
Feel free to request missing tools or give some feedback using our contact form.
Contact Us