29
DKIM Record Explained: What Is DKIM and How Does It Work
Learn what a DKIM record is, how email signatures work, where DKIM public keys are stored in DNS, and how to check and troubleshoot DKIM authentication.
DKIM Record Explained: What Is DKIM and How Does It Work?
Email authentication helps receiving mail servers evaluate whether a message is legitimate. One important method is DKIM, which stands for DomainKeys Identified Mail.
DKIM uses a digital signature to help verify that an email was authorized by a signing domain and that certain parts of the message have not changed after signing. The public key used to verify that signature is published in DNS.
In this guide, you will learn what a DKIM record is, how DKIM works, what a selector means, and how to check your domain's DKIM configuration.
What Is a DKIM Record?
A DKIM record is a DNS TXT record that publishes a public key associated with an email-signing domain and selector. Receiving mail servers can retrieve this key to verify a DKIM signature included in an email.
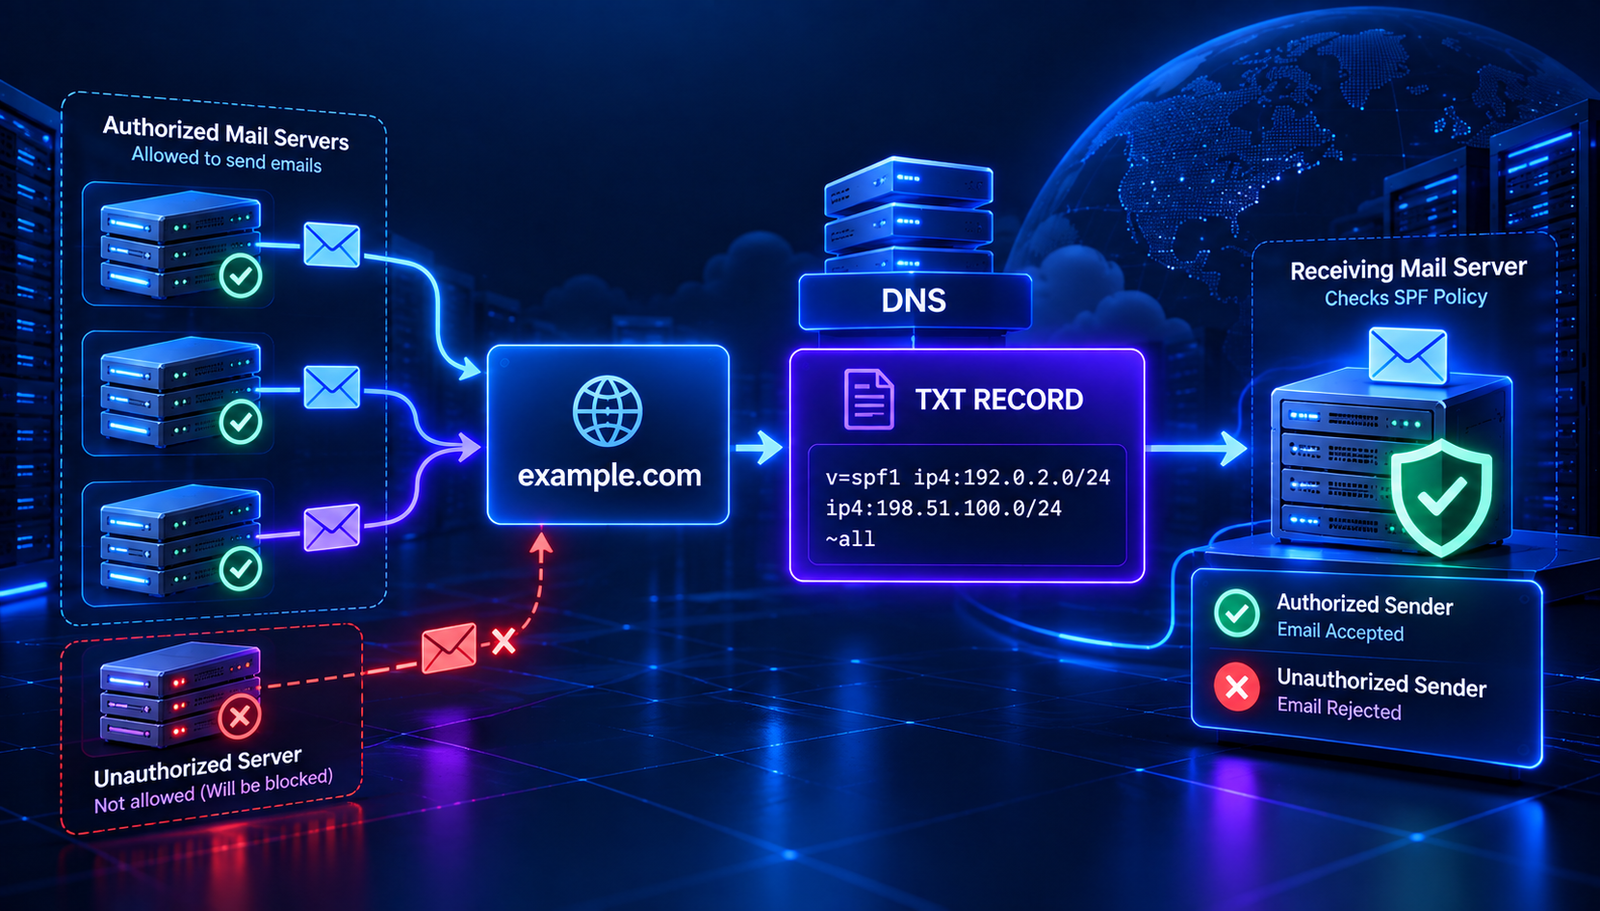
Unlike an SPF record, which describes authorized sending sources, DKIM uses cryptographic signing. The sending service keeps the private key and uses it to sign messages. The matching public key is made available through DNS.
A DKIM record is commonly published at a hostname that combines a selector with the domain's _domainkey namespace.
How Does DKIM Work?
DKIM works through a signing and verification process:
- The sender prepares an email. The sending mail system selects the domain and selector it will use for DKIM signing.
- The message is signed. The sender uses a private key to create a cryptographic signature based on selected message headers and the message body.
- The signature is added to the email. The message includes a DKIM-Signature header with information needed for verification.
- The receiving server reads the signature. It uses the domain and selector in the header to find the corresponding public key in DNS.
- The receiver verifies the signature. It checks whether the signature matches the relevant message content and public key.
If verification succeeds, the receiver can record a DKIM pass result. A pass does not prove that the message is harmless or that the visible sender is trustworthy. It confirms a particular cryptographic check.
What Does a DKIM Record Look Like?
A DKIM TXT record may contain information similar to this:
v=DKIM1; k=rsa; p=PUBLIC_KEY_VALUE
This is a simplified example. The public key value is represented by a placeholder and is not a working key.
Common tags include:
- v: identifies the DKIM record version. When present, the value is DKIM1.
- k: identifies the key type, commonly rsa in many existing configurations.
- p: contains the public key. This is the key material used for verification.
Providers may supply additional tags or use different supported key types. Follow the instructions for the email service that signs your messages.
What Is a DKIM Selector?
A selector identifies which DKIM public key a receiving server should look up. It appears in the DKIM-Signature header as the s= value.
For example, a message might contain:
DKIM-Signature: v=1; d=example.com; s=mail2026; ...
In this example:
- d=example.com is the signing domain.
- s=mail2026 is the selector.
The receiver uses both values to find the public key at a DNS name like:
mail2026._domainkey.example.com
The selector is chosen by the sending service or domain administrator. It is not necessarily the same across different email providers.
Read More: Related DNS Guides
- SPF Record Explained — learn how domains publish authorized sending sources.
- MX Record Explained — understand how DNS directs incoming email to mail servers.
- TXT Record Explained — see how DNS TXT records store verification and policy information.
DKIM vs. SPF: What Is the Difference?
SPF and DKIM help receiving servers evaluate email, but they check different things.
- SPF checks whether the sending IP is authorized by the SPF policy for the evaluated SMTP identity.
- DKIM checks a cryptographic signature associated with a signing domain and selected message content.
SPF can be affected by how email is forwarded because the forwarding server may not be listed in the original domain's SPF policy. DKIM can often survive forwarding if the signed content and headers remain intact, but changes to signed content can cause verification to fail.
Using both methods provides different forms of authentication evidence. Neither one replaces the other.
How to Set Up a DKIM Record
The exact setup depends on your email provider. Many providers generate the selector and public key for you.
- Open your email provider's domain authentication settings. Find the DKIM setup or email authentication section.
- Choose or generate a selector. Some providers assign one automatically. Others let you choose a selector name.
- Copy the DNS details. Your provider should give you the record name or hostname and the TXT value to publish.
- Open your DNS dashboard. This may be your registrar, hosting provider, or external DNS service.
- Create the TXT record. Enter the exact hostname and public key value supplied by the provider.
- Save and wait for DNS updates. DNS caching and TTL settings affect when the record becomes visible.
- Return to your email provider. Use its verification process to confirm that the record is available and DKIM signing is enabled.
Do not create a public key yourself unless you are responsible for managing the signing system. The private key must remain secure and should never be published in DNS.
How to Check a DKIM Record
To check a DKIM record, you need the selector and signing domain. A lookup of the root domain alone may not reveal the DKIM record because it is published under the selector-specific hostname.
For example, if the selector is mail2026 and the domain is example.com, the lookup hostname is:
mail2026._domainkey.example.com
You can query it with:
dig TXT mail2026._domainkey.example.com
Or:
nslookup -type=TXT mail2026._domainkey.example.com
Replace the example selector and domain with the values from your email provider.
You can also use the AuraTools DNS Lookup to inspect DNS information. Enter the full selector hostname and review the TXT result. A visible record confirms that DNS is publishing a value, but you still need to verify that the key matches your provider's configuration and that messages are being signed correctly.
Common DKIM Problems and How to Fix Them
1. Incorrect selector
Problem: You look up a selector that does not match the one used in the email's DKIM-Signature header.
Fix: Inspect a message's DKIM-Signature header and use its s= value with the signing domain in d=.
2. Incorrect DNS hostname
Problem: The record is added under the wrong hostname. This can happen if the DNS dashboard automatically appends the domain and the full domain is entered again.
Fix: Compare the final published hostname with the exact record name supplied by your email provider.
3. Public key value is incomplete
Problem: The TXT value is missing characters or was copied incorrectly.
Fix: Copy the complete value from the provider's setup page. Check whether the DNS dashboard requires a long TXT value to be entered as one string or split into supported segments.
4. DKIM record is published but signing is disabled
Problem: DNS contains a public key, but outgoing messages do not include a DKIM-Signature header.
Fix: Check the email provider's domain authentication settings and make sure DKIM signing is enabled for the sending service.
5. Email content changes after signing
Problem: A mailing system, gateway, or forwarding process modifies signed headers or the message body.
Fix: Review the message path and identify which system is changing the content. Some changes can invalidate a signature, depending on what was signed and how the message was canonicalized.
6. Old keys remain after a provider change
Problem: Your DNS zone still contains a key for a service you no longer use, or the provider has rotated its key.
Fix: Confirm which selectors are currently active. Remove old records only after verifying that no legitimate service still relies on them.
What Is DKIM Key Rotation?
Key rotation means replacing an existing DKIM key with a new one. Email providers may rotate keys as part of their security practices or when you change configuration.
Some systems support more than one selector so that a new key can be published and tested while an older key remains available during a transition. Follow the provider's specific rotation instructions rather than deleting an existing key prematurely.
Keep private keys protected. Anyone with access to a signing private key may be able to create signatures that verify against its corresponding public key.
DKIM and DMARC
DKIM and DMARC are related but serve different roles. DKIM verifies a cryptographic signature. DMARC evaluates whether SPF or DKIM authentication aligns with the domain shown in the message's visible From address.
For DMARC, a DKIM pass alone is not always enough. The signing domain must also meet the required alignment rules for the message to pass DMARC through DKIM.
For a complete email authentication setup, domain owners commonly configure SPF, DKIM, and DMARC together and review authentication results from real messages.
DKIM Best Practices
- Use the exact selector and DNS hostname provided by your email service.
- Publish the complete public key value without accidental changes.
- Keep DKIM private keys secret and restrict access to them.
- Enable signing for every service that sends email using your domain.
- Test actual outgoing messages and inspect their authentication results.
- Follow your provider's key rotation and selector management instructions.
- Use SPF and DMARC alongside DKIM for a broader authentication setup.
- Review DNS records when you change email providers or sending systems.
Frequently Asked Questions
Is DKIM a TXT record?
DKIM public keys are commonly published as DNS TXT records under a selector-specific hostname in the _domainkey namespace.
Where can I find my DKIM selector?
You can usually find it in your email provider's DKIM setup instructions. You can also inspect the DKIM-Signature header of a sent email and look for the s= tag.
Can a domain have multiple DKIM records?
Yes. A domain can publish multiple DKIM public keys under different selectors. This is useful when different email services sign messages independently or when keys are rotated.
Does DKIM encrypt email?
No. DKIM provides a digital signature for authentication and integrity checking. It does not encrypt the email's contents or hide them from systems that handle the message.
Does DKIM passing mean an email is safe?
No. A DKIM pass means the signature verified for the signing domain and signed content. A malicious or unwanted message can still have a valid DKIM signature.
Why does DKIM fail after forwarding?
Forwarding can sometimes modify a message's body or headers. If the changes affect signed content, the receiving server may be unable to verify the original signature.
Conclusion
DKIM helps receiving mail servers verify a cryptographic signature associated with an email's signing domain. Its public key is published in DNS, and the selector tells the receiver which key to retrieve.
To configure DKIM, use the exact hostname and public key supplied by your email provider. Then verify the DNS record and test real outgoing messages. For a more complete email authentication setup, use DKIM together with SPF and DMARC.
Contact
Missing something?
Feel free to request missing tools or give some feedback using our contact form.
Contact Us