25
HTTP Response Headers Explained: A Practical Guide
Learn how HTTP response headers work, understand Cache-Control, Content-Type, HSTS and CSP, and troubleshoot common website configuration issues.
Introduction
A website can load successfully while still having problems with caching, content delivery, redirects, or security configuration. Looking at the page alone does not always reveal what the server is telling the browser.
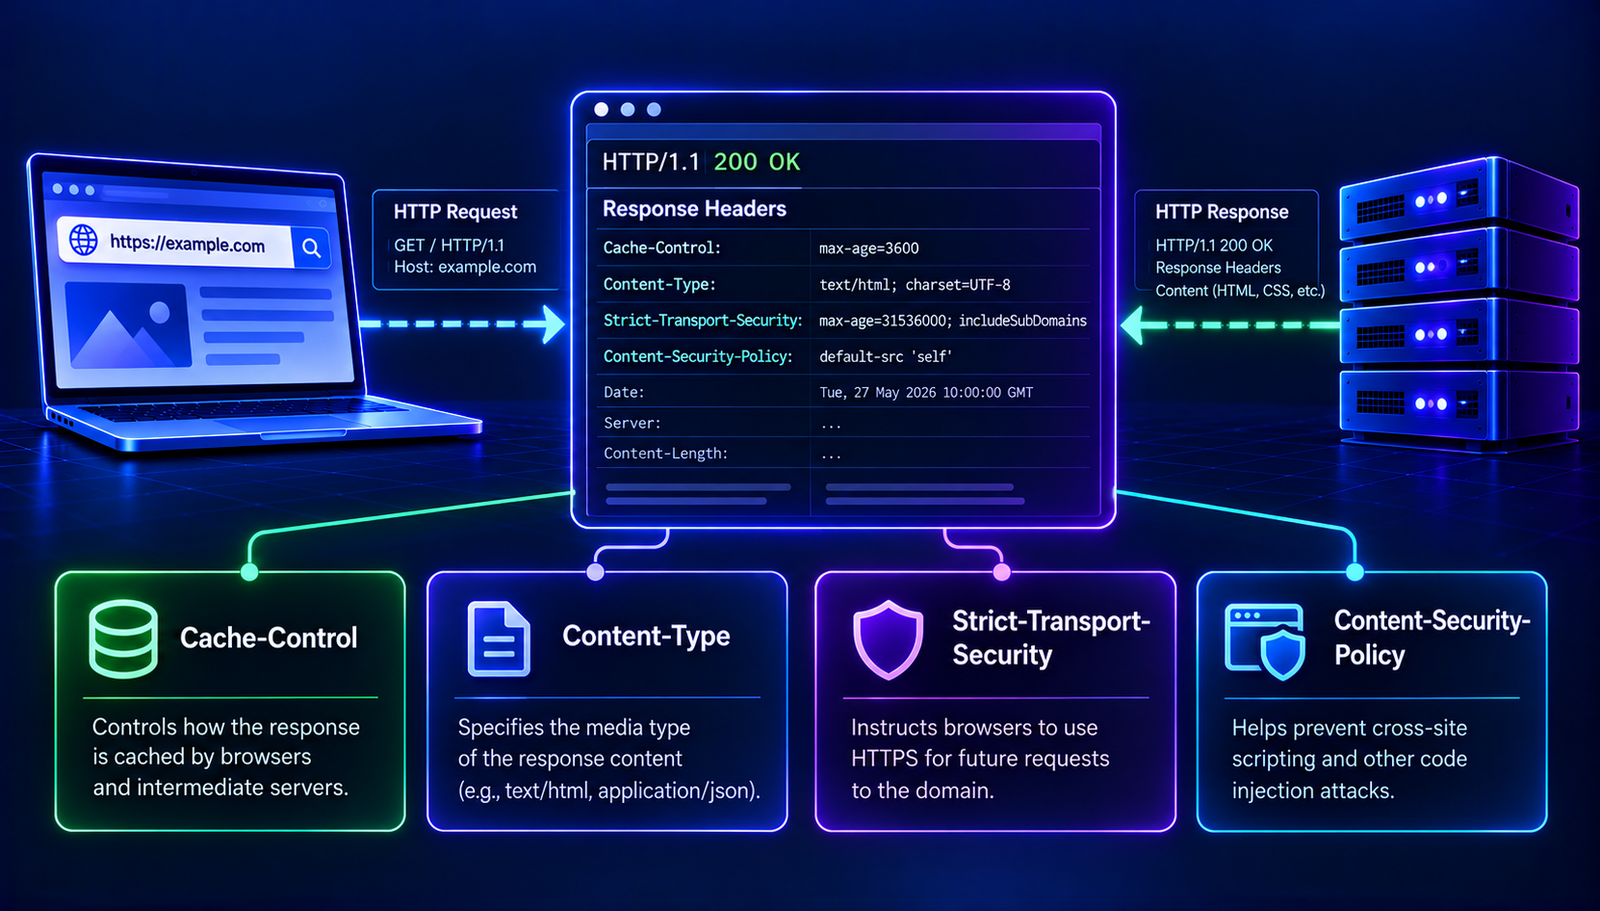
HTTP response headers provide additional information about a server's response. They can describe the type of content being returned, indicate how a response may be cached, control certain browser security behaviors, and communicate other details about the request.
For website owners and developers, understanding these headers can make troubleshooting more precise. Instead of changing server settings at random, you can inspect the response, identify what is actually being sent, and investigate whether the configuration matches your requirements.
This guide explains the most useful HTTP response headers, demonstrates how to inspect them, and shows how to investigate common configuration problems.
What Are HTTP Response Headers?
HTTP response headers are name-value pairs sent with an HTTP response. They provide metadata and instructions related to the response.
For example, a server might return headers like these:
HTTP/1.1 200 OK
Content-Type: text/html; charset=UTF-8
Cache-Control: max-age=300
Content-Length: 1842
This simplified example communicates several things:
- 200 OK is the response status.
- Content-Type identifies the type of content returned.
- Cache-Control provides caching instructions.
- Content-Length indicates the response body's size in bytes when supplied for that message.
These values are illustrative, not the result of a live test. Actual responses depend on the server, application, requested resource, and intermediary services.
HTTP headers can be added or modified by web servers, applications, reverse proxies, and content delivery networks. Therefore, a header seen by a browser may not have originated directly from the application's code.
How to Inspect HTTP Response Headers
You can inspect headers using browser developer tools, command-line utilities, or an online header inspection tool.
Method 1: Use AuraTools HTTP Headers Parser
The AuraTools HTTP Headers Parser provides a convenient starting point for inspecting response headers.
To use it:
- Open the HTTP Headers Parser.
- Enter the URL you want to investigate.
- Run the parser.
- Review the returned headers.
- Identify the specific header related to your problem.
- Verify important findings against the server configuration or browser behavior when necessary.
For example, if you are investigating browser caching, look for Cache-Control. If you want to understand the returned file type, inspect Content-Type.
Important: The results depend on what the tool can retrieve from the target URL. A tool's output may differ from a browser's response because of redirects, request methods, authentication, caching, or server behavior. Do not assume a header is absent from every response just because it is not shown in one inspection.
Method 2: Use Browser Developer Tools
Browser developer tools let you inspect the requests and responses made during an actual page load.
- Open the website in a desktop browser.
- Open Developer Tools.
- Select the Network tab.
- Reload the page.
- Select the main document request.
- Open its headers section.
- Review the response headers.
This method is particularly useful when a website behaves differently across pages or when a specific resource is failing.
Be sure to select the correct request. The HTML document, stylesheet, image, API call, and redirect response can each have different headers.
Method 3: Use curl
If you have access to a terminal, you can inspect response headers with curl.
To request response headers:
curl -I https://example.com/
To follow redirects and inspect the resulting response headers:
curl -IL https://example.com/
The first command sends a headers-only request, which may not behave exactly like a normal browser request. The second follows redirects and displays the header information associated with the redirect chain and final response.
For more detailed request information, you can use:
curl -v https://example.com/
Use care when sharing diagnostic output because verbose logs can contain private URLs, cookies, or authentication details.
Important HTTP Response Headers Explained
1. Content-Type
The Content-Type header identifies the media type of the response body.
For example:
Content-Type: text/html; charset=UTF-8
This indicates HTML content encoded using UTF-8.
Other common media types include:
Content typeTypical use
text/html | HTML documents
text/css | CSS stylesheets
application/json | JSON data
image/png | PNG images
image/jpeg | JPEG images
application/pdf | PDF documents
Why it matters: If a server returns the wrong content type, a browser or application may interpret the response incorrectly.
How to troubleshoot it:
- Confirm the intended format of the resource.
- Inspect the actual Content-Type header.
- Review server MIME-type settings and application response code.
- Check whether a proxy or middleware changes the response.
Do not change a site's content type globally without understanding which file types the server handles.
2. Cache-Control
The Cache-Control header communicates caching directives for browsers and shared caches.
Consider this example:
Cache-Control: max-age=300
This directive indicates that a response can be considered fresh for 300 seconds, subject to the applicable caching rules and other directives.
Other examples include:
Cache-Control: no-cache
This generally means a stored response must be validated before it is reused.
Cache-Control: no-store
This instructs compliant caches not to store the response.
These directives are not interchangeable.
- max-age specifies a freshness lifetime.
- no-cache allows storage but requires validation before reuse.
- no-store directs caches not to store the response.
Practical example: A versioned CSS file that changes only when its filename changes may be suitable for a longer cache lifetime. A page containing sensitive, frequently changing information may require different caching rules.
The right configuration depends on the content and the application's requirements. Incorrect caching can cause visitors to see outdated resources, while overly aggressive caching can create problems when content changes.
3. Content-Encoding
Content-Encoding identifies an encoding applied to the response representation, commonly for compression.
For example:
Content-Encoding: gzip
This indicates that the response uses gzip content encoding.
Compression can reduce the amount of data transferred over the network. However, the presence or absence of this header alone does not establish whether a website is optimally configured.
To investigate compression:
- Inspect the response headers.
- Check whether the client requested a supported encoding.
- Confirm the server or CDN configuration.
- Test the response size and loading behavior under comparable conditions.
You can also use the AuraTools GZIP Compression Test only if the current tool directory exposes the relevant test under a working URL. Verify the actual tool page before adding a direct link to a specific feature.
4. Location
The Location header identifies a destination URL in responses that use it, especially redirects.
For example:
HTTP/1.1 301 Moved Permanently
Location: https://example.com/new-page
In this example, the server indicates that the requested resource has moved permanently to another URL.
The header can also be used in other HTTP workflows, so its meaning depends on the response status and context.
When investigating redirects, inspect both the status code and the destination.
Use the AuraTools Redirect Checker to investigate a URL's redirect path and destination. Check whether the final destination is correct and whether the redirect chain contains unnecessary steps.
5. Strict-Transport-Security
The Strict-Transport-Security header, commonly called HSTS, tells supporting browsers to use HTTPS for future requests to the applicable host for a specified period.
Example:
Strict-Transport-Security: max-age=31536000
This example specifies a one-year HSTS duration in seconds.
HSTS can help reduce the risk of certain protocol downgrade scenarios, but it must be configured carefully.
Before enabling a long duration:
- Confirm that HTTPS works correctly across the intended host.
- Review subdomain requirements.
- Understand how the includeSubDomains directive affects subdomains.
- Do not enable preload-related behavior without reviewing its requirements and operational consequences.
A header inspection tool can show whether the header was returned. It cannot, by itself, prove that every part of the site's HTTPS configuration is correct.
For certificate and HTTPS checks, you can also use the AuraTools SSL Checker.
6. Content-Security-Policy
The Content-Security-Policy header, or CSP, allows a website to define rules governing which resources the browser may load or execute.
For example:
Content-Security-Policy: default-src 'self'
This illustrative policy sets a default source restriction to the site's own origin for directives that fall back to default-src.
A real policy may need separate directives for scripts, styles, images, fonts, frames, and other resources.
CSP can help reduce the impact of certain injection attacks. However, an overly restrictive policy can break legitimate functionality, while a poorly designed policy may provide less protection than intended.
Before deploying a policy:
- Inventory the resources your pages actually require.
- Review external scripts and other dependencies.
- Test the policy in a controlled environment.
- Consider using report-only mode during evaluation.
- Monitor violations before enforcing changes broadly.
Do not copy a complex CSP from another website without adapting and testing it for your own application.
7. X-Content-Type-Options
The X-Content-Type-Options header is commonly used with the value:
X-Content-Type-Options: nosniff
This tells supporting browsers not to perform certain MIME-type sniffing behaviors.
It is particularly relevant when the server needs the browser to respect the declared content type for resources covered by the applicable browser rules.
Before adding this header, verify that your server returns correct content types for scripts, stylesheets, and other resources.
8. Referrer-Policy
The Referrer-Policy header controls how much referrer information browsers include when navigating or requesting resources.
For example:
Referrer-Policy: strict-origin-when-cross-origin
This policy generally sends the full referrer URL for same-origin requests, but limits cross-origin referrer information to the origin under the policy's conditions.
Referrer information can reveal URL paths or query parameters, so the policy should reflect your site's privacy and operational requirements.
Check whether your application depends on referrer information for analytics or other workflows before changing the policy.
9. Permissions-Policy
The Permissions-Policy header lets a site control certain browser features and whether they are available in specified contexts.
The appropriate directives depend on the features your site uses and the browsers you support.
A restrictive policy is not automatically better if it breaks legitimate functionality. Review the site's requirements and test changes before deploying them.
10. Server and X-Powered-By
Some responses include headers such as:
Server: example-server
X-Powered-By: example-platform
These headers may reveal information about the server or application environment.
Their presence and exact values depend on the infrastructure. Proxies and CDNs may modify or remove them.
Reducing unnecessary technology disclosures may be part of a broader security-hardening strategy, but hiding a version string is not a substitute for patching software, securing access, and maintaining a properly configured application.
How to Troubleshoot Common Header Problems
The most useful troubleshooting process begins with a specific symptom rather than a generic list of headers.
Problem 1: Visitors See an Outdated Page or File
Possible cause: A cached response is being reused longer than intended.
What to investigate:
- Inspect Cache-Control.
- Check whether the browser or CDN is serving a cached response.
- Review the resource's versioning strategy.
- Verify that updated content is available at the expected URL.
- Change caching rules only after identifying which cache layer is responsible.
Do not assume that every stale page is caused by Cache-Control. Application caches and service workers may also affect what users see.
Problem 2: A Redirect Goes to the Wrong Page
Possible cause: The server, application, or proxy is returning an unexpected redirect destination.
What to investigate:
- Inspect the status code.
- Review the Location header.
- Follow the redirect chain.
- Check application routing and server rewrite rules.
- Test the final destination separately.
The Redirect Checker can help you examine the redirect path. If the final URL returns an unexpected status code, inspect that response separately using the HTTP Status Code Checker.
Problem 3: A Browser Blocks a Resource
Possible cause: The response may have an incorrect content type, a restrictive content security policy, or another configuration issue.
What to investigate:
- Open the browser's Network panel.
- Select the failed resource.
- Review the response headers.
- Check the browser console for a specific error.
- Identify the exact directive or response value involved.
- Test a targeted correction.
Avoid disabling security controls simply to make the error disappear. Determine which resource is being blocked and whether it should be permitted.
Problem 4: HTTPS Behavior Is Unexpected
Possible cause: The issue may involve certificate configuration, redirects, HSTS, or mixed content.
What to investigate:
- Check the certificate's validity and hostname.
- Review HTTP-to-HTTPS redirect behavior.
- Inspect Strict-Transport-Security when applicable.
- Examine browser console messages for mixed-content warnings.
- Check the response headers of the affected resource.
Use the SSL Checker as one part of the investigation. A successful certificate check does not establish that every application or browser security setting is correct.
HTTP Headers and Website SEO
HTTP response headers can affect how resources are delivered and how clients interact with them, but no single header guarantees better search rankings.
For example:
- Redirect responses can help communicate that a URL has moved.
- Cache headers can influence resource freshness and performance.
- Content types help clients interpret responses correctly.
- Security headers can support safer browser behavior.
- Unexpected server responses can prevent visitors from accessing intended content.
When investigating a technical SEO issue, begin by identifying the affected URL and the behavior you expect. Then inspect its response, redirect path, and page accessibility.
For status-code troubleshooting, use the HTTP Status Code Checker. For header-level investigation, use the HTTP Headers Parser.
Remember that response headers are only one part of technical SEO. Page content, internal linking, canonicalization, crawl accessibility, and indexing signals also matter.
A Practical HTTP Header Audit Checklist
Use this checklist when reviewing a website you own or are authorized to test.
CheckWhat to reviewWhy it matters
Content type | Is the returned media type appropriate? | Helps browsers interpret resources correctly
Cache control | Does the caching policy match the resource? | Helps avoid stale content and unnecessary transfers
Compression | Is supported response compression configured appropriately? | Can reduce transfer size
Redirects | Does each redirect lead to the intended destination? | Prevents broken or unnecessary redirect paths
HTTPS | Are certificates and HTTPS behavior working as intended? | Supports secure connections
HSTS | Is the policy appropriate for the host and its subdomains? | Controls future HTTPS behavior in supporting browsers
CSP | Does the policy allow required resources while limiting unwanted ones? | Helps manage browser resource loading
Referrer policy | Is referrer information limited appropriately? | Supports privacy and operational requirements
Technology disclosure | Are exposed server details necessary? | May reduce unnecessary information disclosure
Error responses | Do important URLs return expected responses? | Helps identify access and availability problems
Record the expected behavior before changing configuration. After making a change, repeat the same test and verify that the application still works.
Frequently Asked Questions
What is the difference between an HTTP request header and a response header?
Request headers are sent by the client to the server. Response headers are returned by the server or an intermediary to the client. They serve different purposes and may use some of the same header names.
Can I inspect HTTP headers without accessing the server?
Yes. You can inspect publicly accessible responses using browser developer tools, curl, or a suitable online utility. However, inspecting a response does not give you administrative access to the server configuration or its internal logs.
Does the presence of a security header mean a website is secure?
No. A header can support a security control, but its effectiveness depends on its value, scope, implementation, and the rest of the application. Security also requires appropriate software updates, access controls, application design, and ongoing maintenance.
Why do headers differ between two requests to the same URL?
Responses can vary by request method, cookies, authentication, negotiated content, cache state, redirects, geographic routing, or intermediary services. Compare the requests and their conditions before concluding that a configuration is inconsistent.
Should I remove the Server header?
Not necessarily. Whether to suppress server-identification headers depends on your environment and operational needs. Reducing unnecessary disclosure may be useful, but it does not replace patching and securely configuring the server.
Can changing HTTP headers improve website speed?
Some header configurations affect caching and compression, which can influence loading performance. Results depend on the resource, server, browser, and network. Measure actual behavior rather than assuming that a particular header automatically makes a site faster.
Conclusion
HTTP response headers reveal important details about how a server delivers content, handles caching, redirects requests, and communicates with browsers.
The best way to use them is to start with a specific problem, inspect the relevant response, and verify the result before changing the configuration. Headers provide useful diagnostic evidence, but they should be interpreted in the context of the application and infrastructure.
For your next investigation, start with the AuraTools HTTP Headers Parser, then use the SSL Checker, Redirect Checker, or HTTP Status Code Checker when the problem calls for a more focused test.
Contact
Missing something?
Feel free to request missing tools or give some feedback using our contact form.
Contact Us